 Rakshastra
An autonomous, AI-driven cyber defense agent designed to map, track, and disrupt digital narcotics operations and illicit bot networks across modern social platforms.
Drug networks hide in plain sight
across social platforms
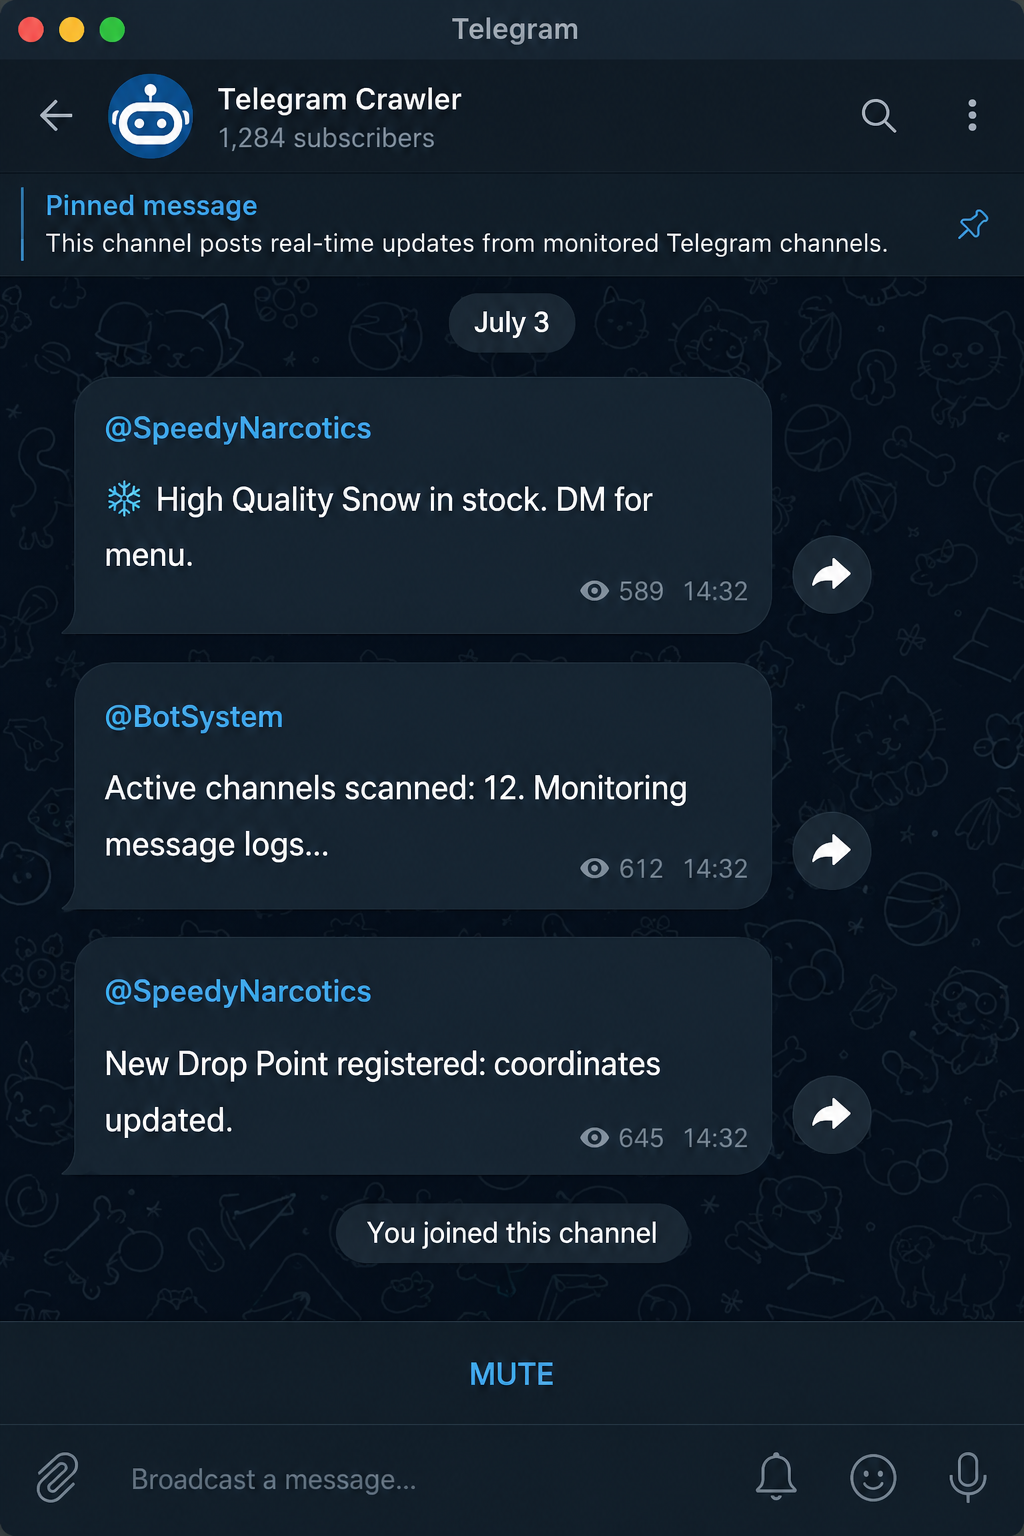
Traffickers exploit Telegram channels, Instagram DMs, and WhatsApp groups to run automated, bot-driven supply chains with menus, pricing, and drop-location delivery.
Invisible Infrastructure
Disposable accounts, coded slang, and emoji-based pricing that evades traditional keyword filters.
Rakshastra's Response
An autonomous AI agent combining Gemini NLP, graph-based identity resolution, and real-time metadata triangulation to build actionable intelligence for law enforcement agencies.
Agent Console
Watch the crawlers ingest, analyze, and triangulate threats in real time.
Core Capabilities
Built on Hermes Agent Core, powered by Gemini Pro, backed by Neo4j Knowledge Graphs.
Implementation Timeline
Five distinct phases designed for robust platform deployment.
Setup & Cloud Infrastructure
Laying the secure foundation for the OSINT ecosystem
Configure security-hardened environments and provision database services with unified identity access management.
Fork the core Hermes codebase and implement continuous deployment via Cloud Build pipelines.
Provision serverless GCP Cloud Run containers running with isolated IAM profiles.
Initialize high-performance Neo4j Graph Database and resilient serverless Firestore instances.
Configure encrypted credential vaults and establish connection tunnels for the Gemini API.
Data Ingestion Pipelines
Connecting live endpoints to ingest high-fidelity intelligence
Establish secure data listeners and scrapers to channel OSINT content directly into automated processing systems.
Deploy custom Telegram API listeners subscribing to public and private investigation streams.
Configure headless Instagram scrapers running through rotating proxy networks to prevent rate limiting.
Build real-time ETL pipelines utilizing structured regex parsing to sanitize raw text blocks.
Map cross-platform identities into the Neo4j threat graph, establishing tracking vectors.
Core Agent Security Skills
Empowering AI agents with logical reasoning and footprint protection
Develop advanced LLM chains to analyze threat contexts safely while keeping agent footprints invisible.
Implement IP isolation layers, Tor-routing wrappers, and mock user agents to hide footprints.
Integrate entity-extraction algorithms targeting phone numbers, crypto wallets, and hidden links.
Design Gemini 1.5 Pro chain-of-thought routing to deduce coordination patterns.
Deploy localized auto-summarization templates to produce rapid incident intelligence reports.
Investigator Dashboard & Alerts
Synthesizing graph networks into visual command centers
Create interactive user interfaces for real-time visualization, query filters, and instant notification systems.
Develop a React-based interactive canvas rendering real-time Neo4j network graphs.
Build tabular search filters querying actors, timestamps, threat weights, and platforms.
Integrate Twilio API handlers to format and dispatch immediate threat alerts directly to WhatsApp.
Configure multi-user access levels ensuring sensitive investigations remain strictly audited.
Pilot Deployment & Optimization
Validating operational stability and scaling output quality
Perform full-scale threat simulations, refine linguistic evaluation parameters, and deploy live integrations.
Simulate cross-platform threat campaigns to analyze end-to-end system response latency.
Finetune context prompts to decrease false positives and raise accuracy of entities extracted.
Secure production endpoints via OAuth2 credentials, strict CSRF mitigation, and session timeouts.
Establish automated feedback loops with partner agencies to continuously refine threat weight rules.
Deploy the Agent
One command install, or download the binary for your platform.
Mac OS
Native client for Apple Silicon.
Windows
Desktop GUI & crawler supervisor.
Linux
Headless CLI agent for servers.
curl -sS https://get.rakshastra.ai/install.sh | bash